02 Engagement model
IT architecture for companies with up to 1’000 employees.
As IT architect, I design a target architecture derived from the processes of your business, not from a vendor catalogue. You receive an architecture picture, a decision log and a roadmap.
01 Topics
Which topics does the target architecture cover?
Every topic starts with the question of which process it carries.
- Identity and access
- Workplace
- Cloud and local operation
- AI with sensitive data
- Data and applications
- Compliance by design
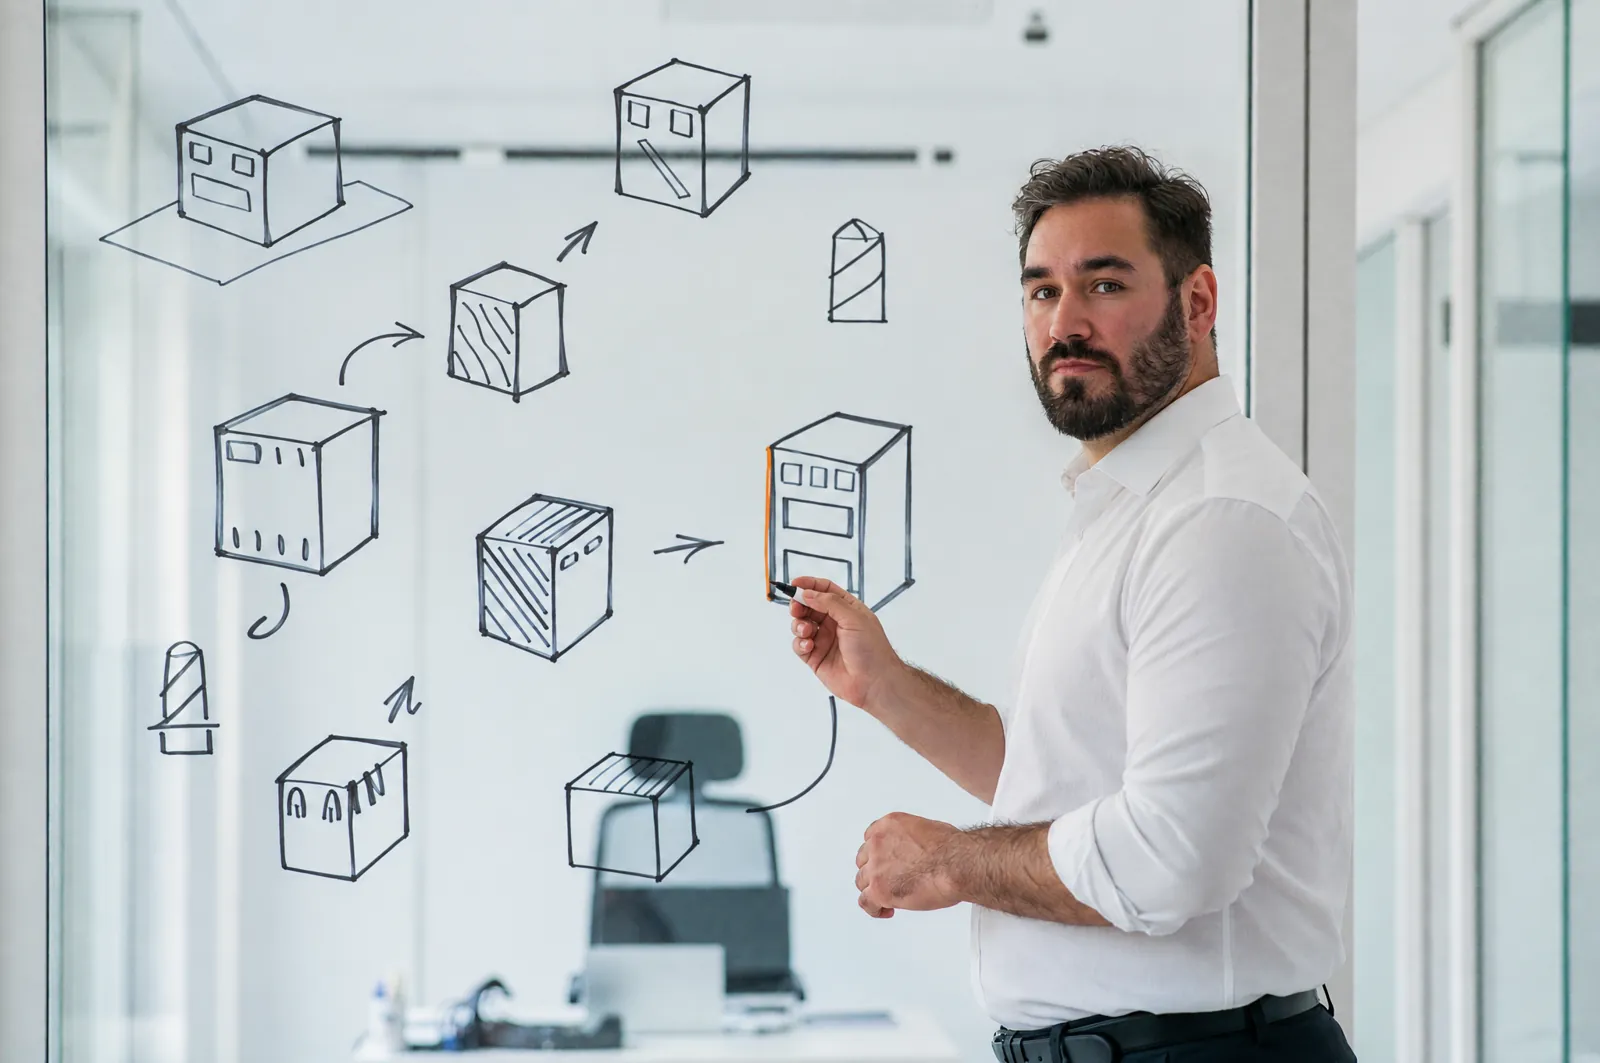
02 Workshop
How is the target architecture created?
In short, intensive rounds with executive management and business units, not in the ivory tower of IT.
03 Artefacts
What is on the table at the end?
- Architecture picturereadable for executive management and IT
- Decision log
- Game planroadmap with effort and costs in relation to the budget
04 Formats
Watch, listen, take away.
The full version of this page: Full text as Markdown
FAQ Answers
Questions about IT architecture.
For which company sizes does Ivo Schönberner work as IT architect?
Mainly for companies with around 50 to 1’000 employees, often SMEs and companies in regulated industries. At this size, IT is too complex for improvisation, but usually has no architecture department of its own.
What is a target architecture?
A target architecture describes what a company’s IT should look like in twelve to 36 months: identities, workplaces, applications, data, operations and security, derived from the processes and goals of the business, with a roadmap to get there.
Does Ivo Schönberner work with Mac and Windows?
Yes. He plans workplaces with Mac and Windows on an equal footing, including device management, identity and security, so that both worlds meet the same rules.
When should AI run locally rather than in the cloud?
When data is confidential, personal or regulated and should not or may not go to third parties. A locally operated model can then be the more sensible choice. The decision depends on data, costs and requirements and is justified in the decision log.
What is compliance by design?
Compliance by design means that requirements such as ISO 27001, the Swiss Federal Act on Data Protection (FADP), the GDPR or sector requirements are built into the architecture from the start, instead of being added later. This saves rework and makes audits plannable.
Does your IT still fit your business?
Thirty minutes, no presentation.
